Sector, size, stack, result.
Projects from Microsoft 365 security work and from govnex’s own agent operations. No customer names, no logos, no tenant details. Click a project to jump to the details.
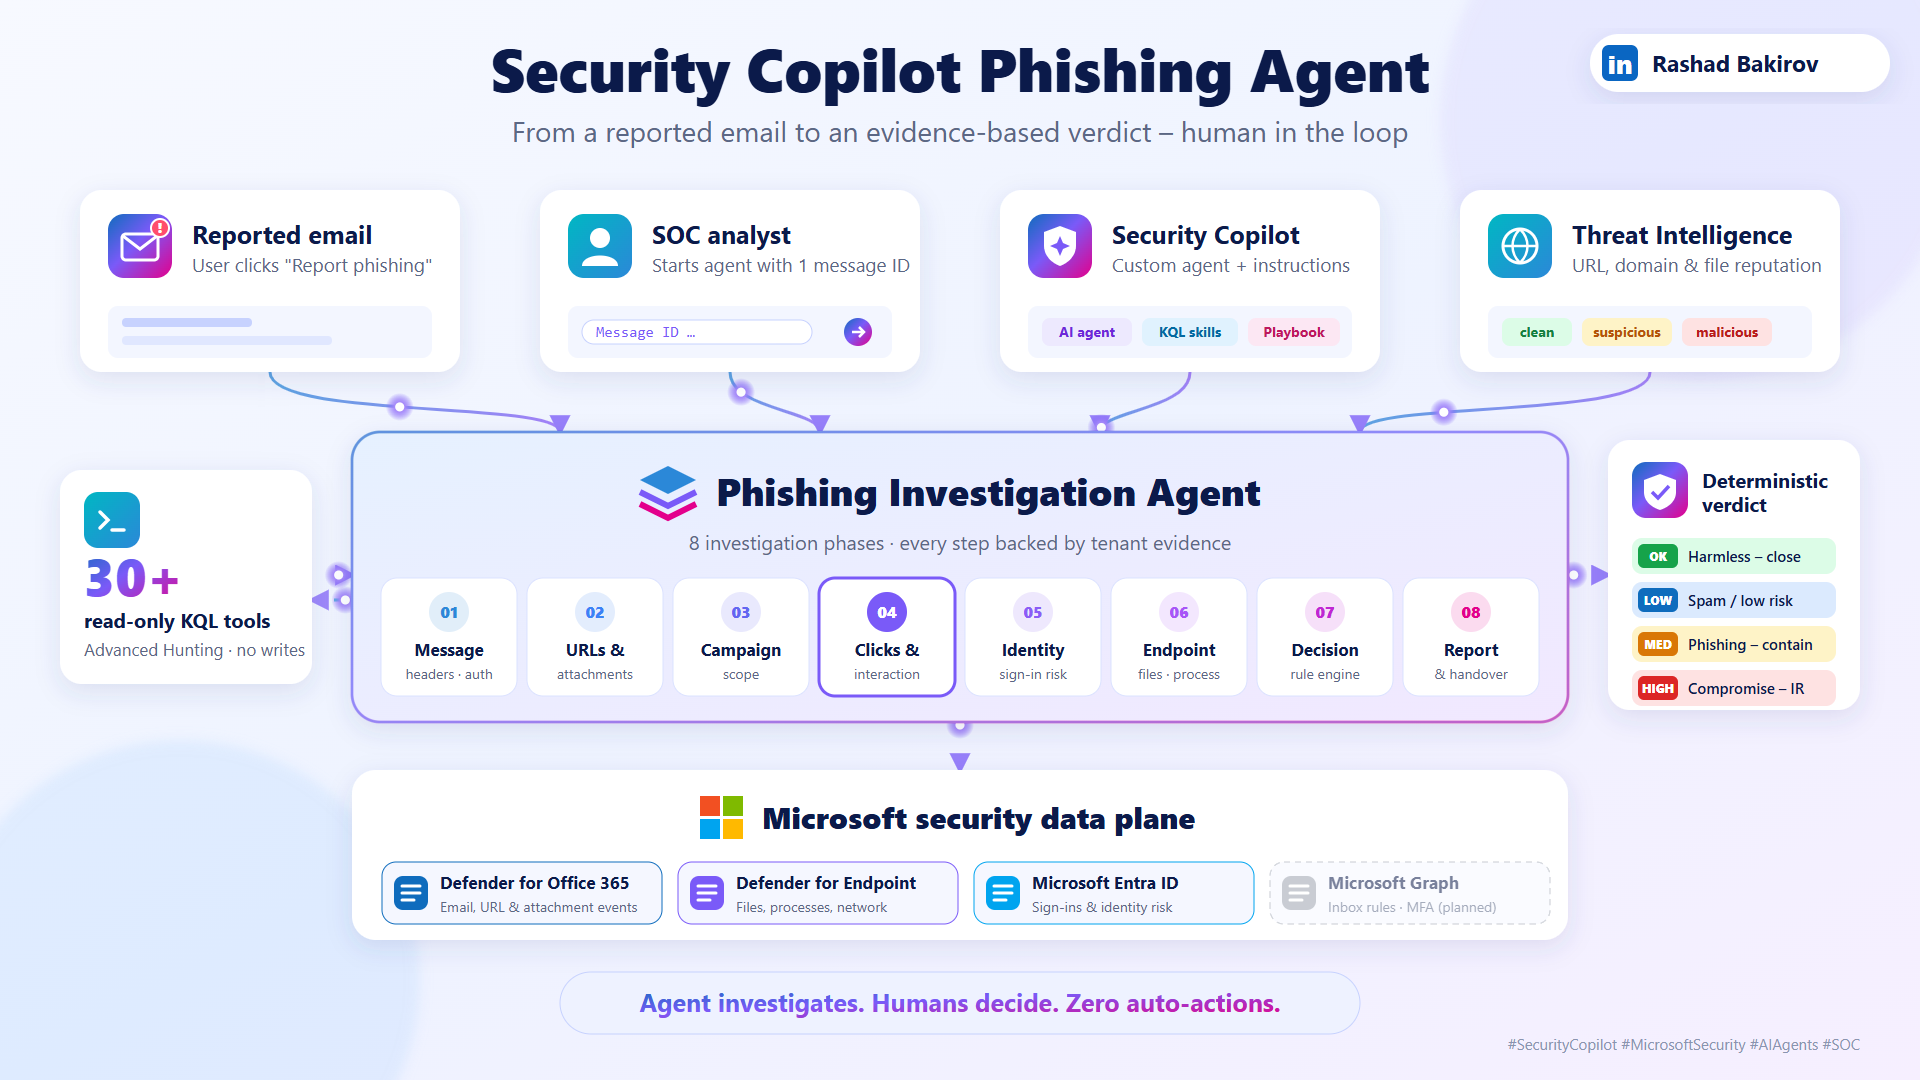
Phishing triage as an agent
Eight phases, 30+ read-only KQL tools, evidence-based verdict.
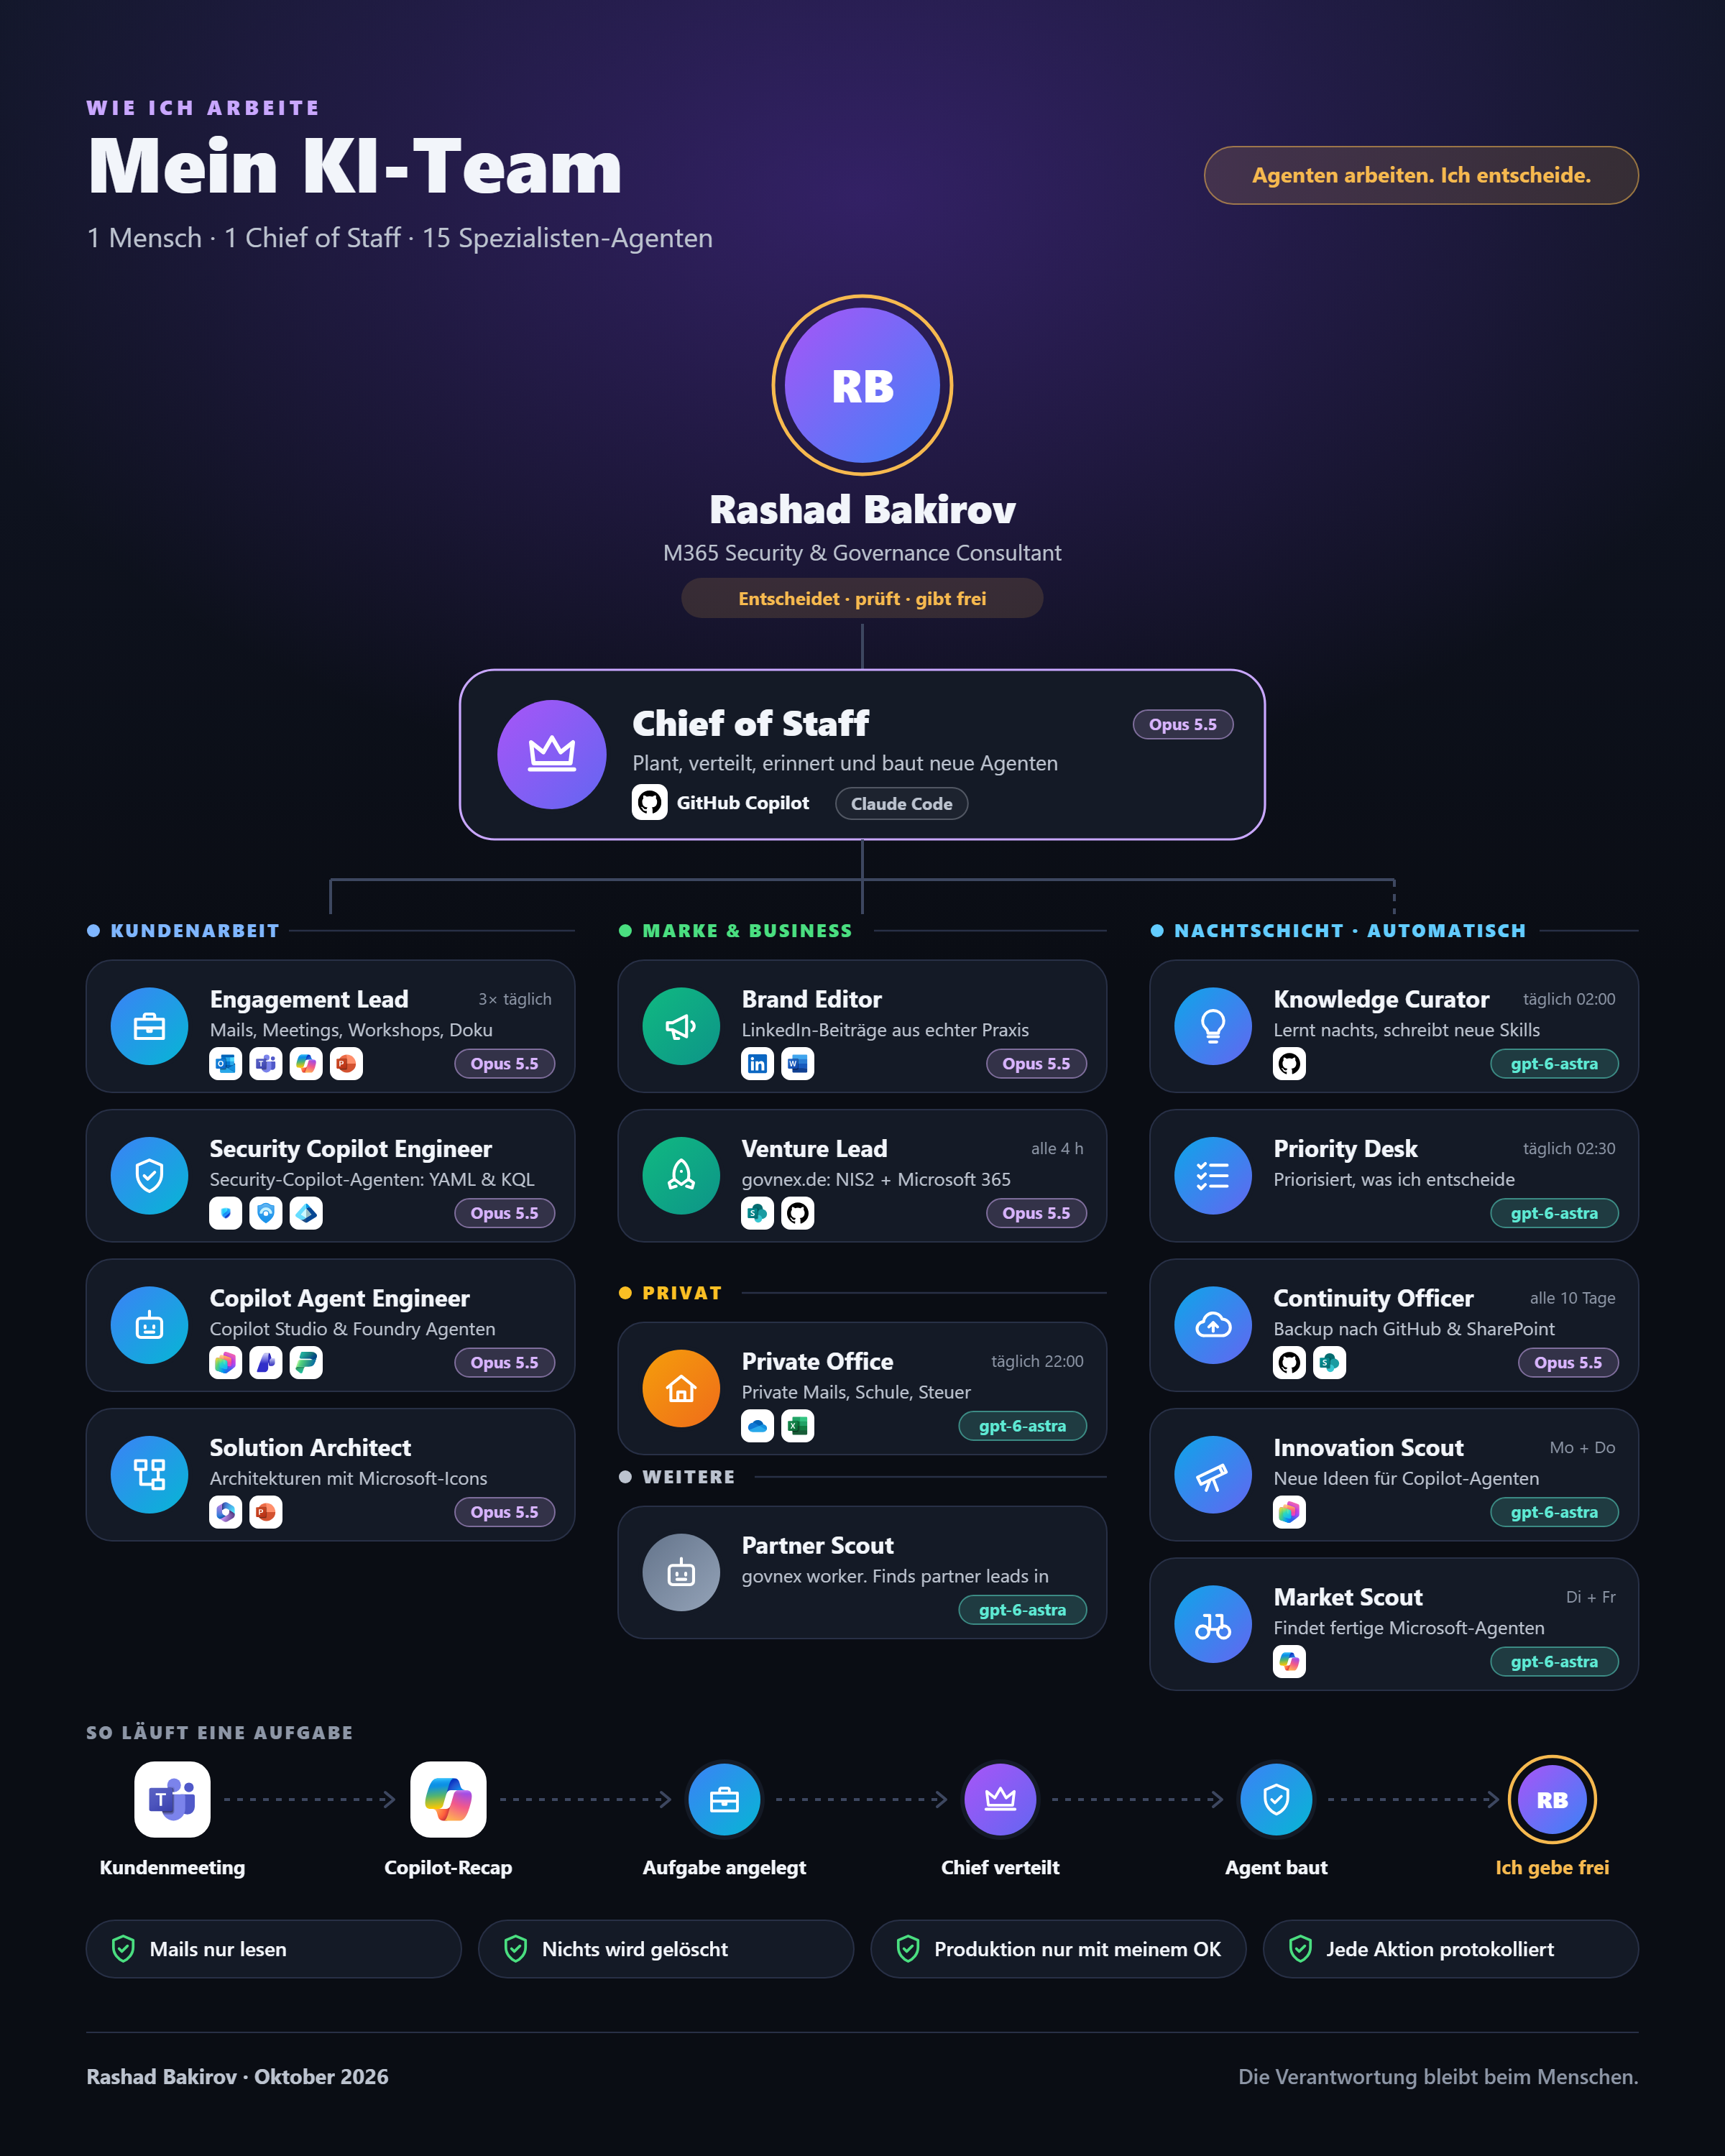
My AI team
One human, one chief of staff, 15 specialist agents.
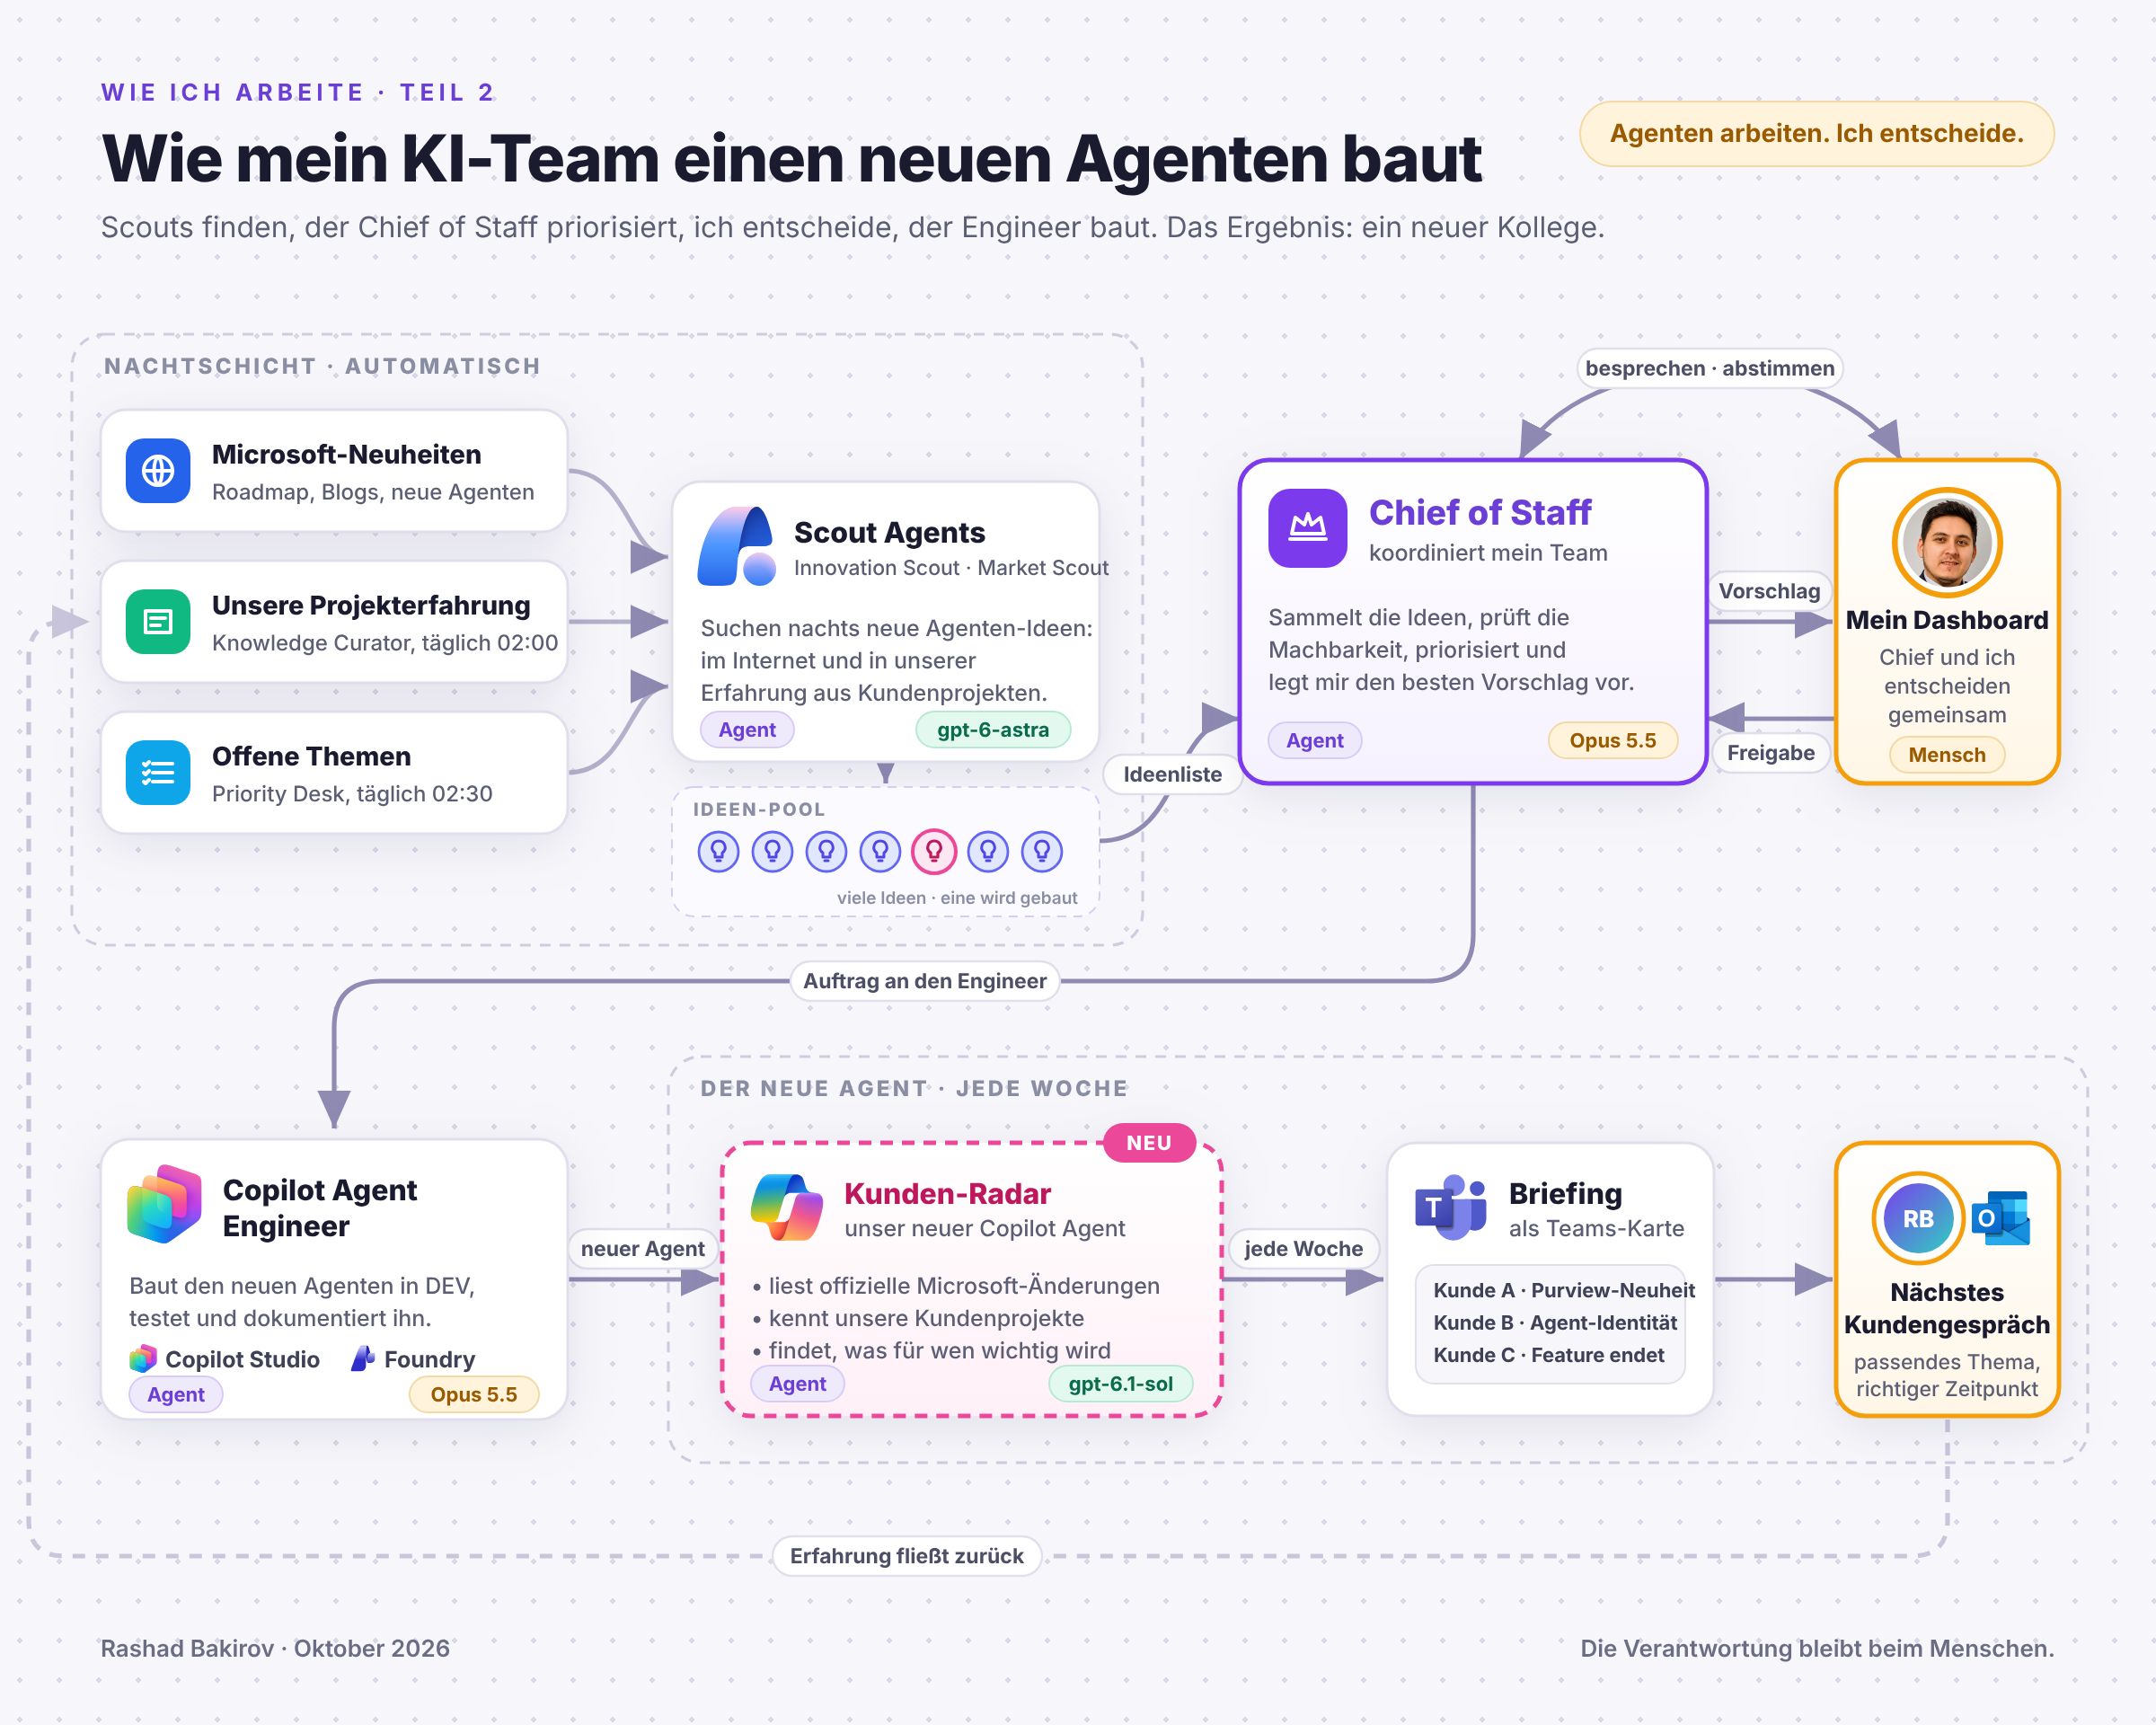
How a new agent is born
Idea, readiness, build, rules, operations.
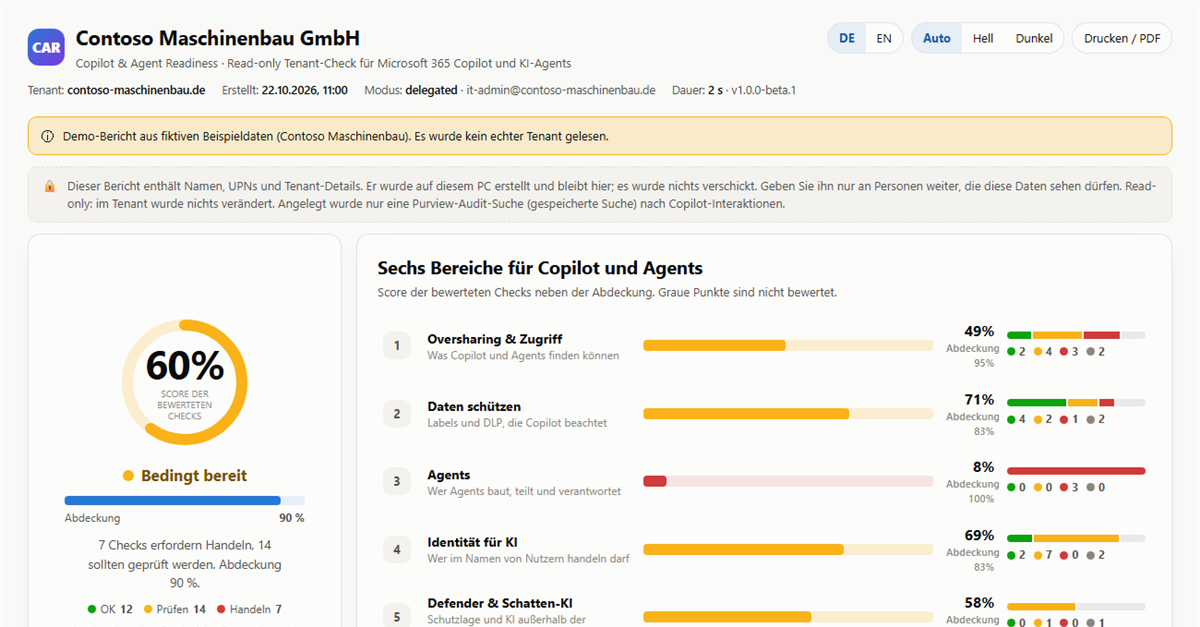
Copilot & Agent Readiness
41 checks, one report, read-only, free.


Customer radar
Microsoft changes assessed per customer.


Copilot rollout packages
Four modules, orderable individually.


From third-party antivirus to Defender
Onboarding in waves, ASR, handover.
Purview rollout as a package
Labels, auto-labeling, DLP, evidence.
Information protection across all workloads
Four labels, DLP, cloud app monitoring.

Zero Trust access model
Conditional Access, session controls, ISO 27001.
Endpoint architecture at scale
Intune, Autopilot, Defender, Zero Trust.
Endpoint and data protection in office and plant
Defender, ASR, DLP, XDR dashboards.
Agents that are in operation.
Copilot & Agent Readiness: 41 checks, one report
A script an admin runs locally: 41 read-only checks in six areas (oversharing and access, protect data, agents, identity for AI, Defender and shadow AI, audit and evidence), delegated Graph sign-in without its own app registration, an HTML report with evidence per finding and a SHA-256 checksum. Every number in the report comes from the tenant.
Customer radar: Microsoft changes assessed per customer
Microsoft announces changes to Microsoft 365, Copilot, Purview and Defender every week. The agent reads the announcements from official sources, assesses them against a customer’s profile (licences, services in use, open projects) and writes a short weekly brief: what affects you, what to do, by when. Own tools and official Microsoft sources only.
Copilot rollout packages for a partner
A partner needed a proposal for its end customer that describes Copilot not as a licence but as a rollout. Result: four modules, orderable individually. Readiness & oversharing, data protection (labels, DLP for Copilot, DSPM for AI, rollout in waves), governance & operations (audit, retention, eDiscovery, agent rules) and agents in three sizes (SharePoint agent, Copilot Studio with Power Automate, Foundry with external systems). Plus adoption and a quarterly managed service.
Projects the agent work stands on.
Migration from third-party antivirus to Defender
A retailer with several sites replaced its existing antivirus. Device onboarding in waves through Intune, replacement in passive mode, then switch-over, Attack Surface Reduction first in audit, then in block mode, compliance-based access to Microsoft 365, handover to operations with a runbook.
Purview rollout as a repeatable package
Label taxonomy with four levels, auto-labeling for financial and personal data, DLP for Exchange, SharePoint, Teams and OneDrive with test and enforcement phases, foundations for Insider Risk, audit and evidence for internal audit. Documented as a package with fixed work steps so it can be transferred to further entities.
Information protection across all workloads
Label taxonomy (Public, Internal, Confidential, Highly confidential), auto-label policies, DLP in everyday workflows, Defender for Cloud Apps to monitor sharing and app activity, continuous compliance reporting.
Zero Trust access model for Exchange, SharePoint and Teams
Risk-based Conditional Access policies, session controls through Defender for Cloud Apps, Identity Protection with MFA and sign-in risk, mapping of controls to ISO 27001 and regulatory expectations.
Endpoint architecture and rollout at scale
Intune MDM with Autopilot for Windows devices, Entra join, staged enrolment, role-based compliance and configuration baselines, Defender for Endpoint policies, operations runbook, admin training, alignment with Zero Trust.
Endpoint and data protection in office and plant
Defender for Endpoint and Intune for office and production devices, replacement of the old antivirus, ASR rules, compliance-based access, Purview DLP for sensitive data, XDR dashboards for the operators.
Similar starting point?
The AI readiness check shows where you stand in three minutes. The intro call settles the rest.